Inside CVE-2026-124194: The silent Outlook NTLMv2 credential-hash zero-day
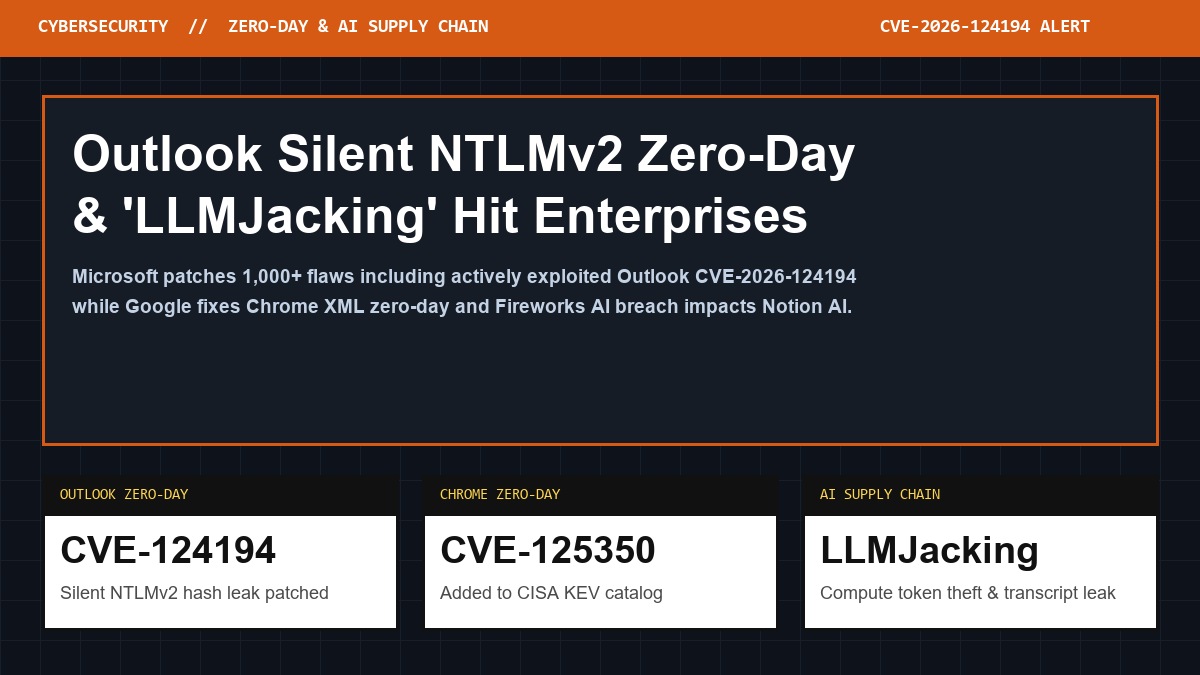
Topping Microsoft’s November 2026 security bulletin — which resolved more than 1,000 vulnerabilities across Windows, Exchange, Office, and Azure — is CVE-2026-124194, a critical spoofing and credential-disclosure vulnerability in Microsoft Outlook that attackers exploited in the wild prior to patch release.
By crafting a specially formatted email payload, threat actors bypassed Outlook’s automatic external-content block and forced the victim’s machine to initiate an outbound SMB authentication handshake to an attacker-controlled server — silently handing over NTLMv2 credential hashes without requiring the user to click a malicious link or open an attachment.
Chrome CVE-2026-125350 and the Fireworks AI–Notion "LLMJacking" fallout
In parallel, CISA ordered federal agencies to patch CVE-2026-125350, a high-severity use-after-free zero-day in Google Chrome’s XML/XSLT parser actively weaponized by commercial spyware and APT groups. Enterprise CISOs are also auditing third-party AI inference vendors after an "LLMJacking" attack against model-hosting provider Fireworks AI — designed to hijack compute tokens and unauthorized LLM access — resulted in unauthorized exposure of a small percentage of Notion AI user chat transcripts.
- Microsoft patched CVE-2026-124194 after confirming active in-the-wild exploitation leaking NTLMv2 hashes via Outlook.
- Google patched Chrome XML zero-day CVE-2026-125350, and Notion disclosed limited transcript exposure tied to the Fireworks AI incident.
- Which specific threat group first weaponized CVE-2026-124194 prior to the November Patch Tuesday release.
- ✓Sources: written from primary sources and official statements, linked above.
- ✓Fact-check: names, dates and claims checked against the original sources.
- ✓AI use: researched with AI tools; written and reviewed by our editors. Our AI policy
- ✓Independence: UpdateNext has no financial relationship with the companies covered.